Technical Due Diligence Services
Before you write the cheque, Hygge reads the code. Our technical due diligence covers architecture, code quality, security exposure, and the team behind it, and returns a report your investment committee can act on in two weeks.
What the Review Covers
The areas that decide whether the technology you are buying into holds up. Each one gets a rating and the evidence behind it.
Architecture and Scalability
Whether the system survives ten times the current load, and what it costs to get there. Many products work fine at present volume and need a rewrite at the scale the business plan assumes.
Code Quality and Maintainability
A structured code audit covering test coverage, complexity, duplication, and dependency health, translated into how fast a new engineer could ship their first feature.
Security Exposure
Known vulnerabilities, secrets in the repository, access control gaps, and dependency risk. A single unpatched library in a regulated product changes the valuation conversation.
Technical Debt and Roadmap Cost
What the promised roadmap will cost to deliver on this codebase, which is often the gap between the pitch and the reality.
Team and Key-Person Risk
Who wrote what, how much knowledge sits with one person, and what happens to delivery if they leave the week after close.
IP, Licensing and Compliance
Who owns the code, which open-source licences are in use, and whether any of them create obligations the buyer would inherit.
What Gets Agreed Before the Review Starts
Hygge sets scope in a short call, because a due diligence for a seed investment and one for an eight-figure acquisition are different pieces of work.
The call settles each of these:
- Deal context, investment, acquisition, or internal decision, since each one weights the findings differently.
- Depth, a focused two-week review or a full software due diligence covering every system.
- Access, what the target will grant and how the review works around whatever they withhold.
- Deadline, tied to your close date, working backwards from it.
- Fixed scope and price, agreed before anyone opens the repository.
When Buyers and Investors Call Us
The situations behind most projects Hygge runs.
A report says the platform is finished, and the numbers behind that claim are missing. Technical due diligence checks the code, the build and the data model, and answers finish or rebuild with evidence. One week, before the money moves.
You Are Investing and the Product Is the Company
The team is impressive and the demo works. Whether the thing underneath supports the growth plan is a separate question, and it decides whether this round funds product or a rebuild.
You Are Acquiring and Inheriting the Codebase
After close it becomes your maintenance cost, your security exposure, and your engineering roadmap. Finding out afterwards has no remedy.
The Roadmap Looks Too Fast for the Codebase
The plan promises six major features next year. Whether this architecture can carry them at that pace is answerable now, with evidence.
The Engineering Team Is Two People
Concentrated knowledge is a real risk to price into the deal, and it is invisible on a cap table.
A Portfolio Company Keeps Missing Delivery
Every quarter the roadmap slips and the explanations are technical. An independent read tells you whether it is the code, the team, or the plan.
How the Review Runs
Two weeks of software due diligence, from access granted to a report in your inbox.
Scoping Call
Deal context, depth, deadline, and price, settled before work starts.
Access and Automated Analysis
Repository access, then static analysis, dependency scanning, and security tooling across the codebase.
Manual Review
Senior engineers read the core systems by hand, because the parts that matter most are the parts tooling scores poorly.
Team Interviews
Sessions with the target's engineers on architecture decisions, known problems, and what they would fix first.
Report and Walkthrough
A written report with ratings and evidence, plus a call where your team can ask questions of the people who did the work.
What the Report Changes About the Deal
You get a written verdict with the reasoning attached, so a board decision rests on findings. Where the answer is finish, the remaining work is listed and costed. Where it is rebuild, you know that before the next payment. Buyers usually arrive looking for a software audit company before an investment, an acquisition or a decision to keep building on what exists. The answer they need is what it will cost to run this codebase for two more years, and what would have to be replaced first.
What the Assessment Puts in Writing
The report goes to whoever is deciding: your board, an investment committee, or the buyer on the other side of the table.
Where a Codebase Review Moves the Price
Sectors where what the engineering team built decides what the company is worth.
Healthcare & Staffing
Health data handling, access records, and vendor exposure checked before an acquirer inherits the liability.
Sales & Marketing Technology
Integration debt across the revenue stack, and how much of the roadmap is blocked by it.
Real Estate & PropTech
Portal dependencies and data ownership reviewed, since a feed that can be revoked changes the valuation.
Retail & E-Commerce
Peak-season readiness measured against the last two seasons of incident history.
EdTech
Institution contracts, accessibility compliance, and the cost of the platform work they still require.
Media & Entertainment
Rights handling, licensing logic, and the parts of the catalog the software cannot legally serve.
LegalTech
Privilege boundaries and retention behavior verified in code, not in the policy document.
Logistics & Warehouse Automation
Hardware coupling and site-specific logic that decide whether the system ports to a second warehouse.
Systems Hygge Has Assessed and Built
Products where Hygge worked at the architecture level, on both sides of the review.
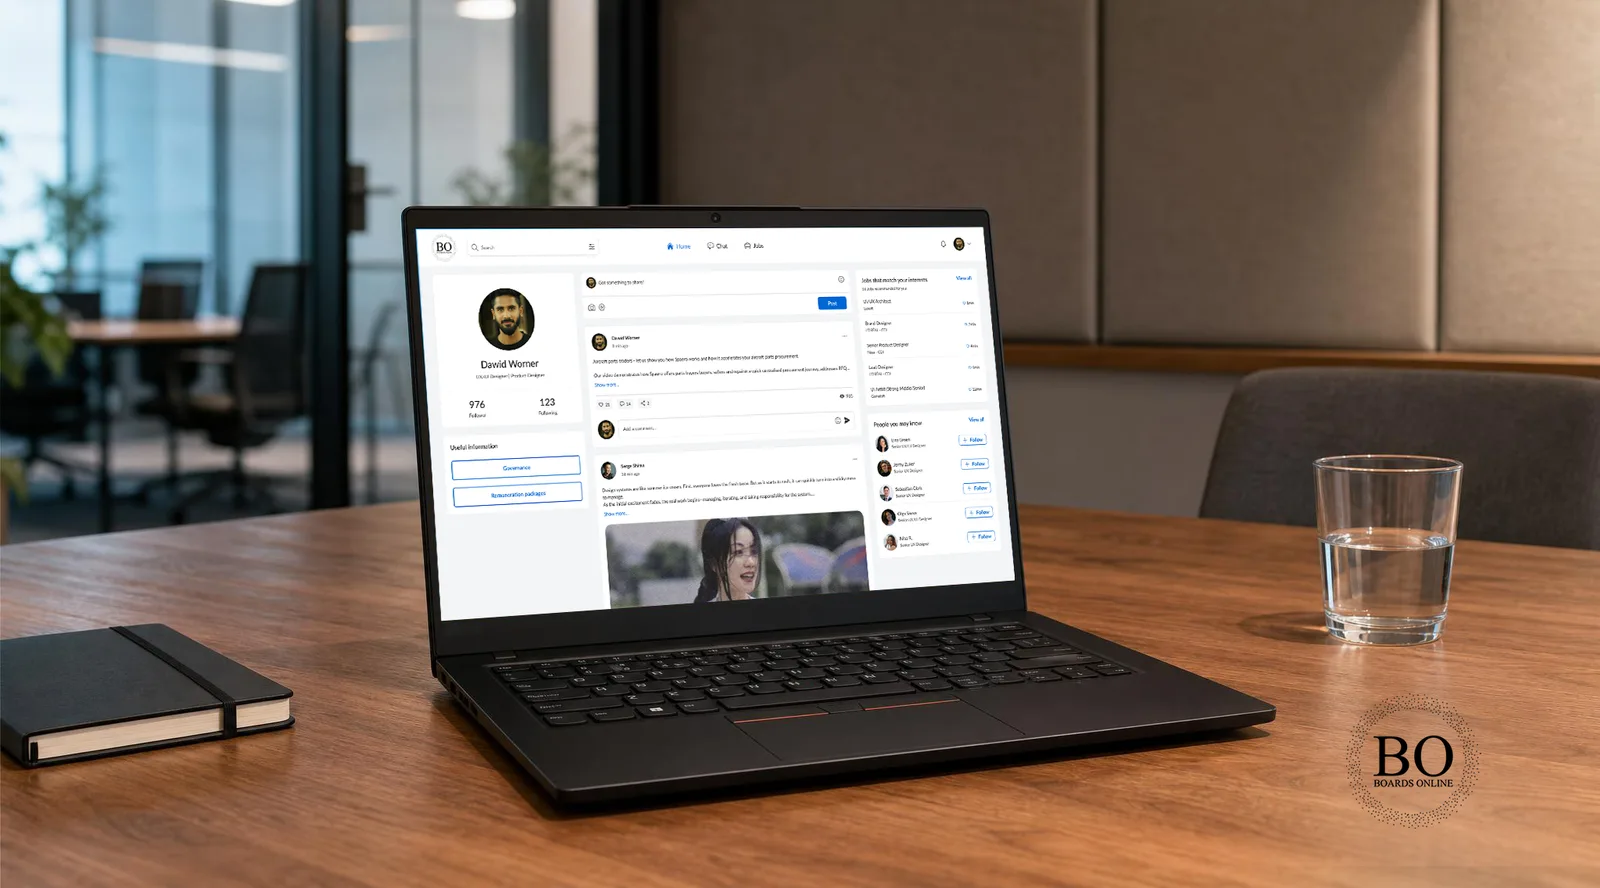
BoardsOnline
A founder had paid for a platform that reports said was finished. An audit showed what worked, and the rebuild started from there.
- 3 bucketsSorted features a status report called done
- ~6 monthsFrom that audit to a stable platform
- 1+ yearOf support past the original contract
What You Get in the Report
A rating and the evidence for each of the six areas, a costed remediation list, the key-person risks named, an assessment of whether the roadmap is deliverable on this codebase, and a walkthrough call with the engineers who did the work.
How We Assess
Automated coverage across the whole codebase, manual review where the value and the risk concentrate.
Complexity, duplication, and coverage measured across the codebase, turning a maintainability opinion into numbers an investor can read.
 SonarQube
 CodeQL
 Semgrep
 GitHub Actions
Frequently Asked Questions
What investors and acquirers ask before commissioning a review.
 Why is technical due diligence important?
What is due diligence in M&A?
What is operational due diligence?
What is technical due diligence?
How much does technical due diligence cost?
How long does a technical due diligence take?
What does a technical due diligence report include?
What are the red flags in a code audit?
Do I need technical due diligence before acquiring a company?
Who performs technical due diligence for investors?
What does a technical due diligence review cover?
From an Unknown Codebase to a Priced Risk
Tell us about the deal and the close date. You get a scope, a price, and a report your committee can use.
Tell Us Which Codebase You Are Assessing
Share the company, the deal timeline, and what you need answered before the money moves.
Get a First Consultation
We review the repository, team, and delivery history for anything that would change scope, cost, or timeline.
Receive a Detailed Proposal
A scoped plan with the approach, timeline, and cost, built around your deal timeline.