Penetration Testing Services
Most companies book a test because a customer, an auditor or an incident set the date. Hygge tests with your source open. Every finding comes with the line of code behind it, a fix, and a report you can send.
What Penetration Testing Services Cover
Hygge scopes the surfaces that carry your data and your money. The rest stays out of the price.
Web Application Penetration Testing
Login, sessions, and what one role can reach that belongs to another. This is where a customer sees somebody else’s data.
API Penetration Testing
Authorisation checks, token scope, rate limits. One missing check hands over a whole table in a single request.
Mobile App Penetration Testing
Keys shipped inside the binary, local storage, certificate pinning. Anyone can pull your app apart on their own laptop.
Cloud Accounts and Identity
How far one stolen credential travels. This is where a small foothold turns into everything you run.
Connected Devices and Firmware
Provisioning secrets, update channels, physical access. One unit taken off a wall can expose the whole fleet.
Scanning Left in the Pipeline
Dependency and secret scanning wired into CI with thresholds set. Your next release gets checked without booking anybody.
What Gets Agreed Before Anyone Touches Anything
Hygge scopes from the reason you need the test. Price and report date are fixed before it starts, and the retest is inside the price.
Scoping puts each of these in writing:
- The target list: domains, APIs, mobile builds, cloud accounts, hardware in the field.
- The roles testers work from, and whether they start with credentials or from outside.
- Test windows, rate limits and a named contact, so nothing fires while your customers work.
- What counts as critical for your business, so severity matches your own exposure.
- An exact price and a report date, with the retest inside both.
When Software Security Testing Stops Being Optional
Each one has a deadline and a price tag.
A security questionnaire lands mid-deal. An auditor sets a date. A customer asks what happens if one tenant reaches another. The money is already on the table. The test is what keeps it there.
A Deal Is Waiting on a Report
The questionnaire asks for a test from the last twelve months. Procurement will not move without one. The contract sits until somebody produces it.
The Audit Date Is Already Set
SOC 2 or ISO renewal has a fixed window. Test, fix and retest all have to happen inside it, or the certificate lapses.
Something Already Got Through
A strange login. A user who saw somebody else’s data. Leadership wants to know what else is open, and a guess will not do.
Four Hundred Findings, No Priority
A scanner produced a wall of output. Most of it is noise. Two sprints went into sorting it, and the real hole is still open.
Two Years of Shipping, Zero Testing
Auth, payments, file uploads, partner integrations. All live, all handling somebody’s data, none ever attacked on purpose.
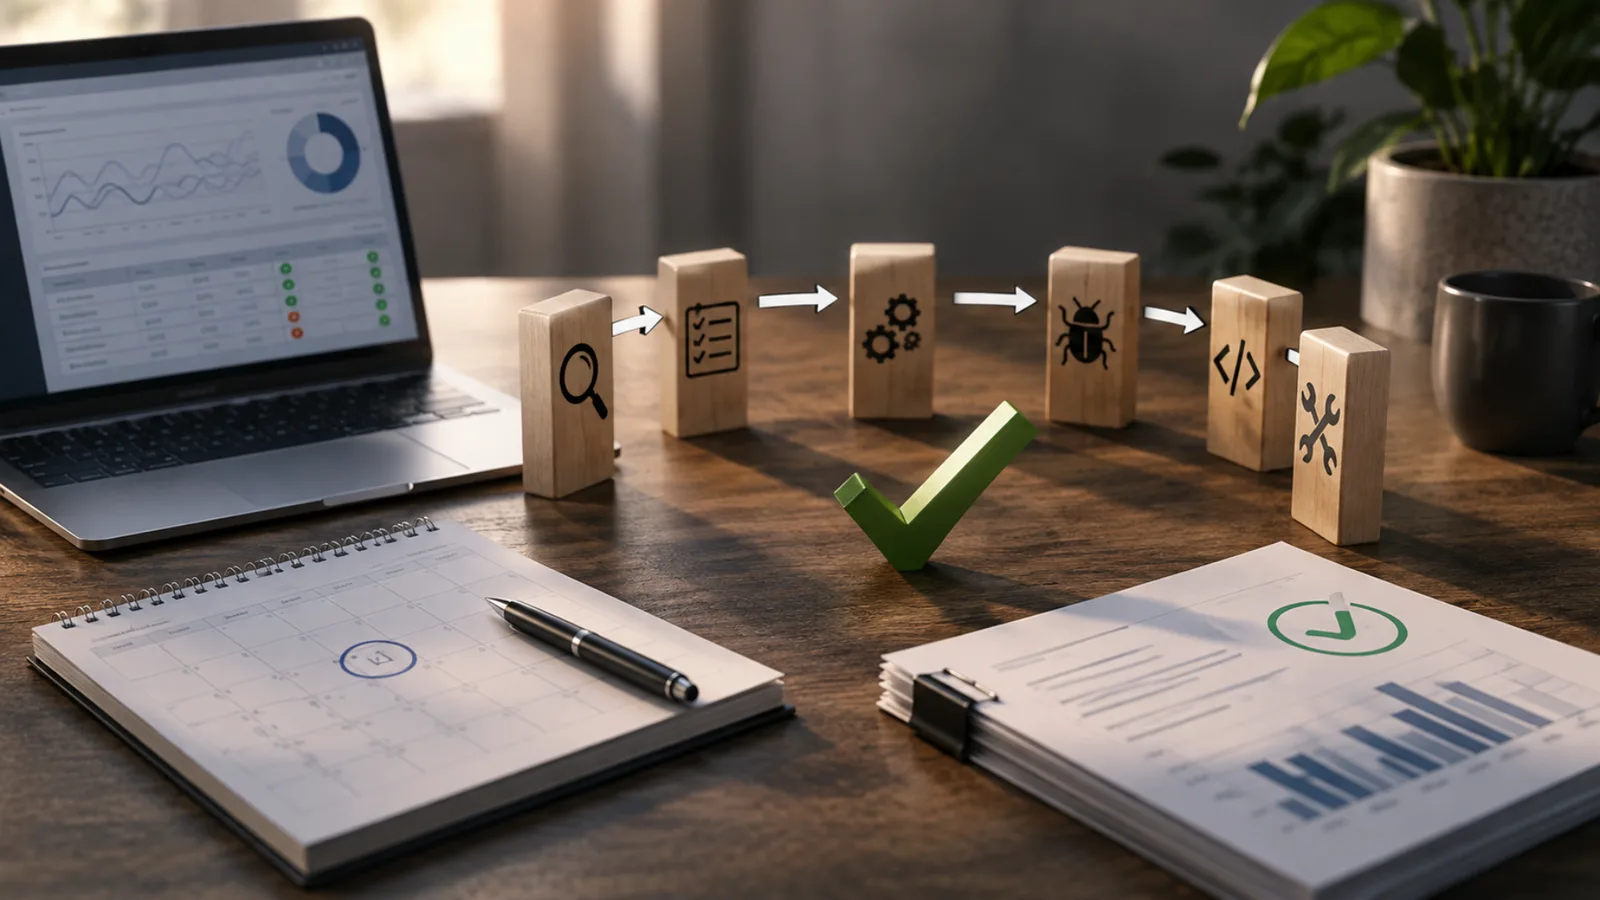
How Penetration Testing Services Run End to End
One week from a signed scope to a report your customer or auditor accepts.
Agree Scope and Rules
Day 1Targets, roles, test windows and the escalation path, signed by both sides.
Map the Surface
Day 2Every domain, endpoint, role and account in scope, listed so nothing gets hit by accident.
Test With the Source Open
Days 3 to 5Testers work with your code in front of them. A finding gets confirmed at the line that causes it.
Report With Reproduction
Day 6Steps, request, file and line for every finding, plus a fix your engineers can ship alone.
Retest What Was Fixed
After your fixEach fix attacked again and confirmed in writing, inside the price you agreed.
What Changes After the Test
Your deal moves. Procurement gets the report they asked for, with a date and a named tester on it. Your engineers stop guessing. Each finding comes with the steps to repeat it and the file to change. Next year is easy. The retest confirms the fix in writing, so the same finding stops coming back. A penetration testing company earns its fee on the findings that surprise you. Security testing services cover the standard surface, while mobile app penetration testing and API penetration testing go after the two places most breaches now start. Software security testing runs alongside the build, so a finding is caught while it is still a change, so a finding is a change in the next release and never a rewrite.
The Standards Security Testing Services Are Held To
Every number here is agreed with you before work starts, then measured against how things run today.
Where Someone Will Ask for the Report
Sectors where a test result is a document a customer or auditor reads.
Healthcare & Staffing
Health platforms tested before an enterprise health system signs, with findings mapped to their questionnaire.
Retail & E-Commerce
Payment and checkout paths tested against the card industry requirements your acquirer enforces.
Sales & Marketing Technology
Multi-tenant platforms tested for cross-account access before an enterprise procurement review.
LegalTech
Legal platforms tested where a confidentiality breach ends the client relationship.
Public Safety & Security
Systems handling sensitive records tested with the access model as the primary target.
Real Estate & PropTech
Property platforms holding identity documents and financial records tested end to end.
EdTech
Education platforms tested against institutional security requirements before a contract renews.
Aviation
Operational systems tested inside the network segmentation a regulator expects.
Platforms Holding Sensitive Records
Work where the data being handled set the security bar.
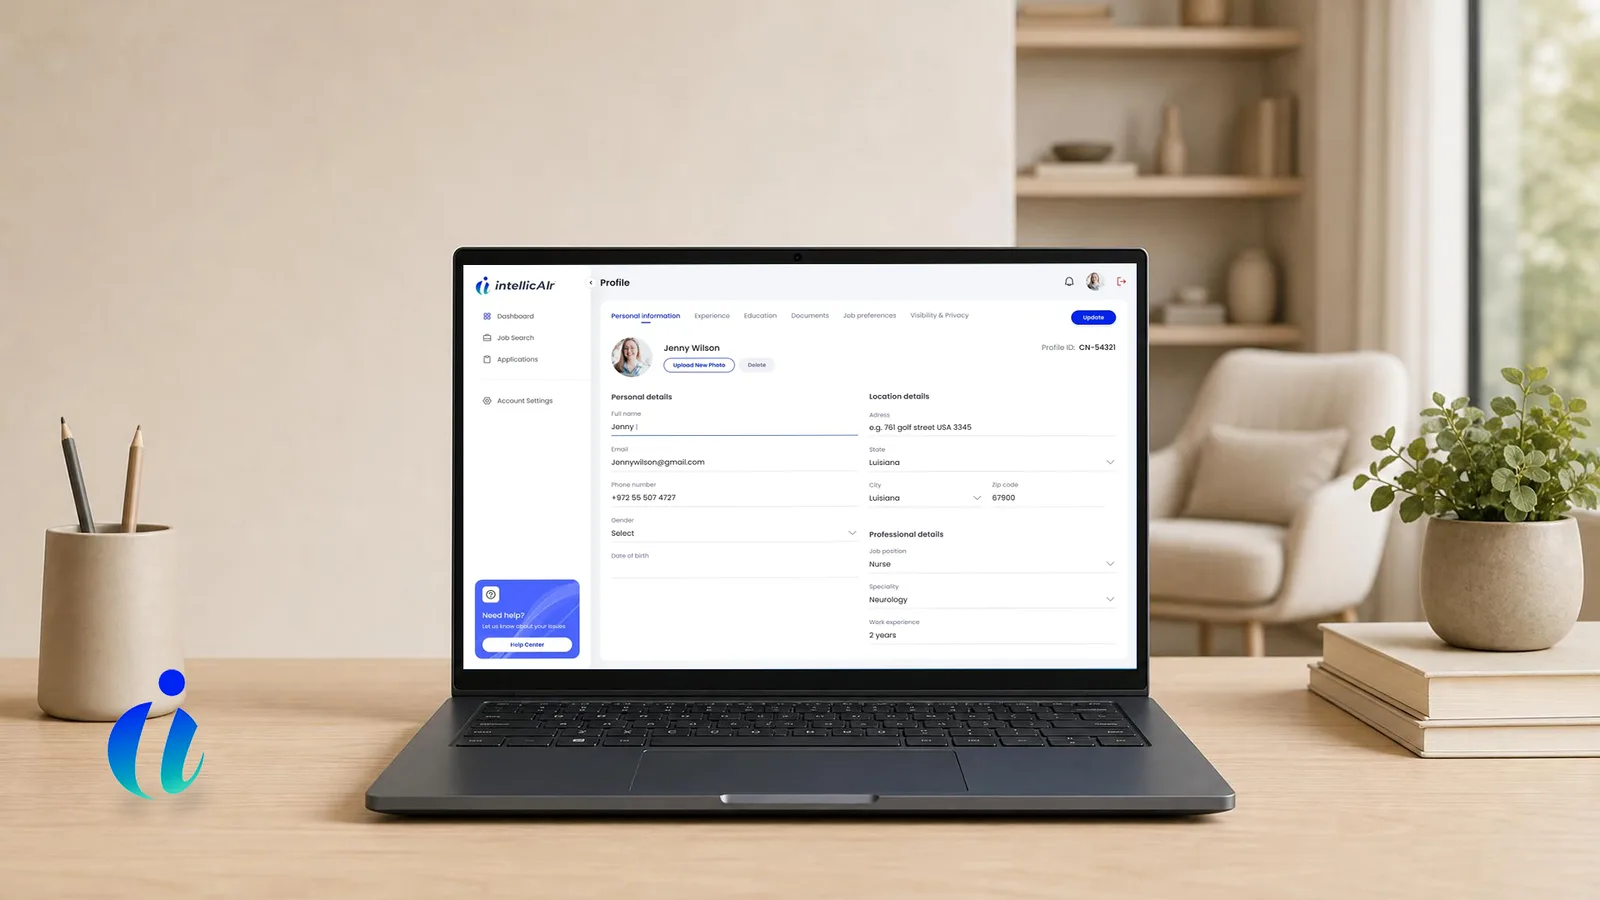
IntellicAIr
A two-sided nurse staffing marketplace built around a sealed bidding system written from scratch for how these facilities buy.
- 1 roundFills what sat open for 78 days
- No nameOn a bid that used to hide a 40 % cut
- 1 inviteBrings a facility’s own agencies onboard
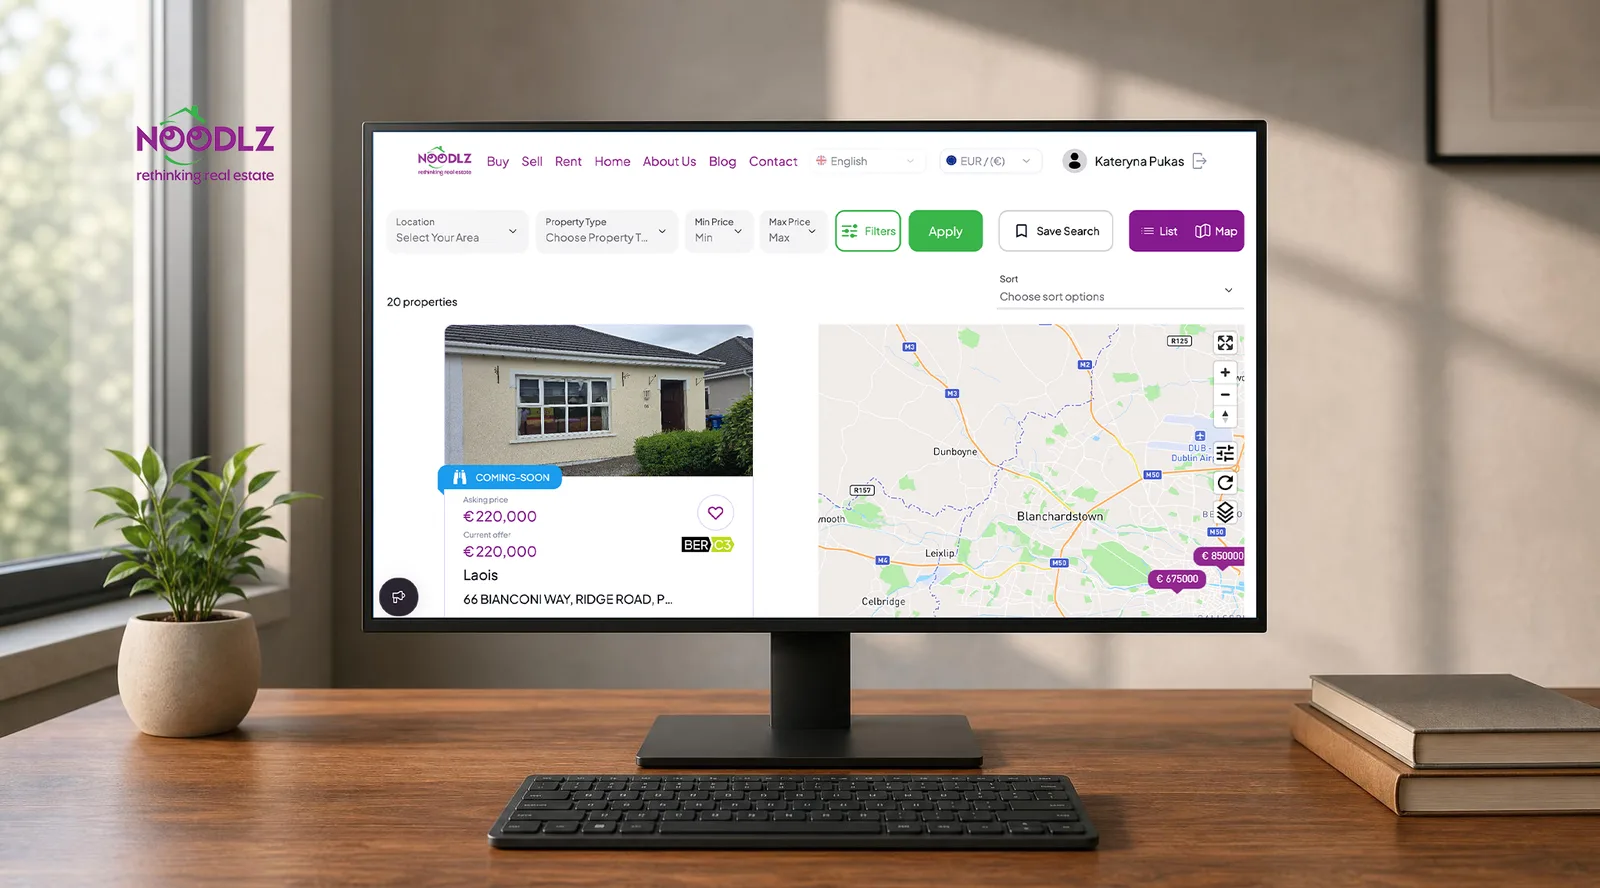
NOODLZ
A property platform covering the full agency lifecycle, from listing through live auction bidding to a document vault, built across sixty-plus weekly sprints.
- 1 platformReplaces auctions run outside any system
- 1 vaultReplaces contracts moving between inboxes
- 2+ yearsOf continuous delivery since 2024
A Report You Can Send the Same Day
Every finding with the steps to repeat it, the file behind it, and a fix your team can ship. A summary for the customer or auditor who asked. A retest once the work is done.
What Application Security Testing Reaches
The layers Hygge tests against, and where the exposure usually turns up in each one.
Testing against the running app, logged in, following the paths an attacker would take. Every finding reproduced step by step.
 Burp Suite
 OWASP ZAP
 Postman
 REST APIs
Penetration Testing and Vulnerability Assessment Services: FAQ
What vulnerability assessment services cover, what they produce, and when to run one.
 What is penetration testing?
What does penetration testing do?
Why do penetration testing?
When is penetration testing most effective?
How long does a penetration test take?
What does security testing cover?
How is a penetration test scoped?
How often should we test?
Do you test production or a staging copy?
What does the report contain?
Do you retest after fixes?
What does a penetration test cost?
What do pen testing services include?
From a Contract Clause to a Report You Can Send
Tell Hygge who is asking for the test and by when. You get a scope, a price and a report date the same week.
Tell Us What Needs Testing
Share the application, the environments, and the compliance deadline driving the request.
Get a First Consultation
We review your scope, environments, and reporting needs for anything that would change scope, cost, or timeline.
Receive a Detailed Proposal
A scoped plan with the approach, timeline, and cost, built around your actual test scope.