Security Consulting Services
A threat model built around your system, a read of the architecture and the code behind it, and a remediation plan ordered by what an attacker can reach from outside. Hygge's security consulting services end in work your engineers can start, with each item carrying the exposure it closes.
What Application Security Consulting Covers
The parts that turn a list of findings into an order of work. Security consulting services at Hygge scope which of these your system needs after mapping what is exposed.
A Threat Model Built Around Your System
Who would want in, what they would want, and the paths that reach it from the internet, from a compromised account, and from a device in the field. Threat modeling services give the rest of the work its priority order.
Architecture and Trust Boundaries
Where data crosses a boundary, which service trusts which, and what one compromised component would reach from the position it holds. A security architecture review works at the level where that trust was granted.
Code Read Against Real Attack Paths
Authentication, authorisation, input handling, secrets, and the places where a request from one tenant can touch another. Security code review focused on the paths the threat model marked as reachable.
Cloud and Identity Configuration
Roles, network boundaries, key management, logging, and public exposure across your accounts. Cloud security consulting covering the settings that decide how far a stolen credential travels.
Connected Devices in the Field
Provisioning, credential rotation, firmware update paths, and what a physically accessible device gives away. IoT security services for fleets already deployed and running.
Remediation Ordered by Reach
Every finding carried through to what it exposes, how it gets fixed, and how long that takes, so the plan is read by severity of reach and by effort together.
What a Security Assessment Settles
Hygge opens with an assessment of what your system exposes, who can reach it, and what the business would lose in each case. Security assessment services quoted from a read of the architecture, with the price agreed before remediation work is scoped.
The assessment produces each of these:
- A map of the attack surface: what is public, what is reachable with valid credentials, and what sits behind a device in the field.
- A threat model naming the actors that matter for your business and the paths available to each.
- Findings from the code and the configuration, each traced to the asset it exposes.
- A remediation plan ordered by reach and effort, with an owner suggested for each item.
- The evidence an enterprise customer or an auditor asks for, and the gaps between your written policy and what the system does.
What Puts Security on the Roadmap
The situations behind most enquiries Hygge scopes.
A customer sent a security questionnaire, credentials sit in the repository, and everyone has production access. Security consulting closes those in the order that carries risk. The audit traces every answer back to the system.
A Customer Sent a Security Questionnaire
Two hundred questions arrived with the contract, and answering them truthfully means finding out what the system does today. The deal is waiting on it.
Credentials Are in the Repository
A key was committed years ago, rotated nowhere, and still works. Nobody knows the full list of what else is in the history.
Everyone Has Production Access
Access was granted as people joined and stayed as they moved on. There is no record of who used what, and a leaver still has a working token.
A Device Fleet Is Already Deployed
Hardware sits in places anyone can touch, with credentials baked in at manufacture and an update path that was designed for convenience.
The Auditor Asked for Evidence
The controls exist in a document and partly in the system, and nobody can produce a log showing that either one held last quarter.
How We Run Cloud Security Consulting
From mapping what is exposed to a plan your engineers can work through, with each finding traced to the asset behind it. This is how security consulting services run at Hygge.
Map the Attack Surface
Public endpoints, cloud accounts, third-party integrations, and anything physical in the field. The map is built from what the accounts and the DNS serve today, which is where the first surprises show up.
Build the Threat Model
Actors, motives, and the paths available to each, agreed with the people who know what the business would lose. This is what turns findings into priorities.
Read the Code and the Configuration
Authentication and authorisation paths, tenant isolation, secret handling, and cloud roles. Application security consulting that follows the threat model into the repository.
Rank by Reach
Each finding placed against what it exposes and what it costs to close, so the first week of work removes the most reach.
Hand Over and Recheck
The plan, the evidence, and a recheck of the items closed, so the remediation has a record behind it when a customer asks.
What Changes After the Review
The questionnaire gets answered from evidence, so a deal stops waiting on security review. Access, secrets and audit logging move into the architecture, which is what an auditor asks to see next year. A security assessment is usually the first project: what is reachable from where, which accounts still exist, and what a reviewer will ask that nobody has an answer for. The output is a list somebody can act on, ordered by what it would cost you if it were used.

What Security Consulting Gives Back
These are the targets the work is built to hit, measured on your own numbers.
Where a Security Question Blocks the Deal
Sectors where a customer, an auditor, or a regulator asks before they sign.
Healthcare & Staffing
Health data handling, access records, and breach response reviewed against what regulators expect.
LegalTech
Privilege boundaries, retention, and client confidentiality verified in the running system.
Retail & E-Commerce
Payment flows and customer data reviewed against card industry requirements.
Sales & Marketing Technology
Tenant isolation and data residency answered before an enterprise procurement team signs.
Public Safety & Security
Access control down to the record, with an audit trail that survives an internal review.
Aviation
Operational systems reviewed against aviation regulator requirements and supplier audits.
Media & Entertainment
Content protection and entitlement enforcement checked against rights-holder obligations.
EdTech
Student data handling and institutional security questionnaires answered with evidence.
Systems Built Around Access Rules
Work where who can reach which record was part of the architecture.
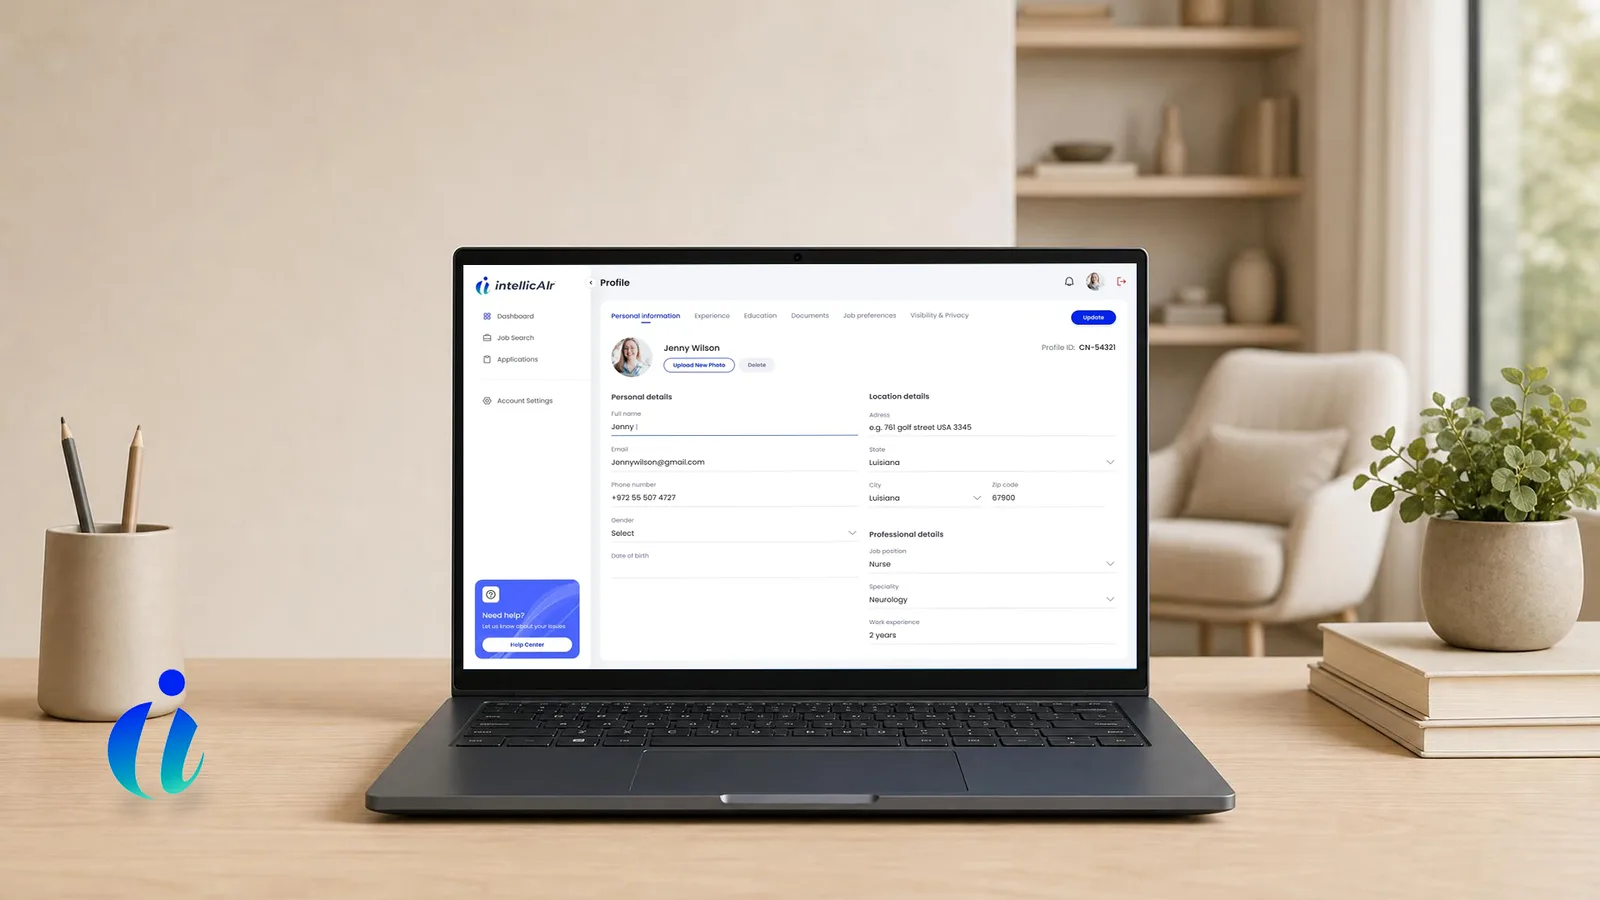
IntellicAIr
A two-sided nurse staffing marketplace built around a sealed bidding system written from scratch for how these facilities buy.
- 1 roundFills what sat open for 78 days
- No nameOn a bid that used to hide a 40 % cut
- 1 inviteBrings a facility’s own agencies onboard
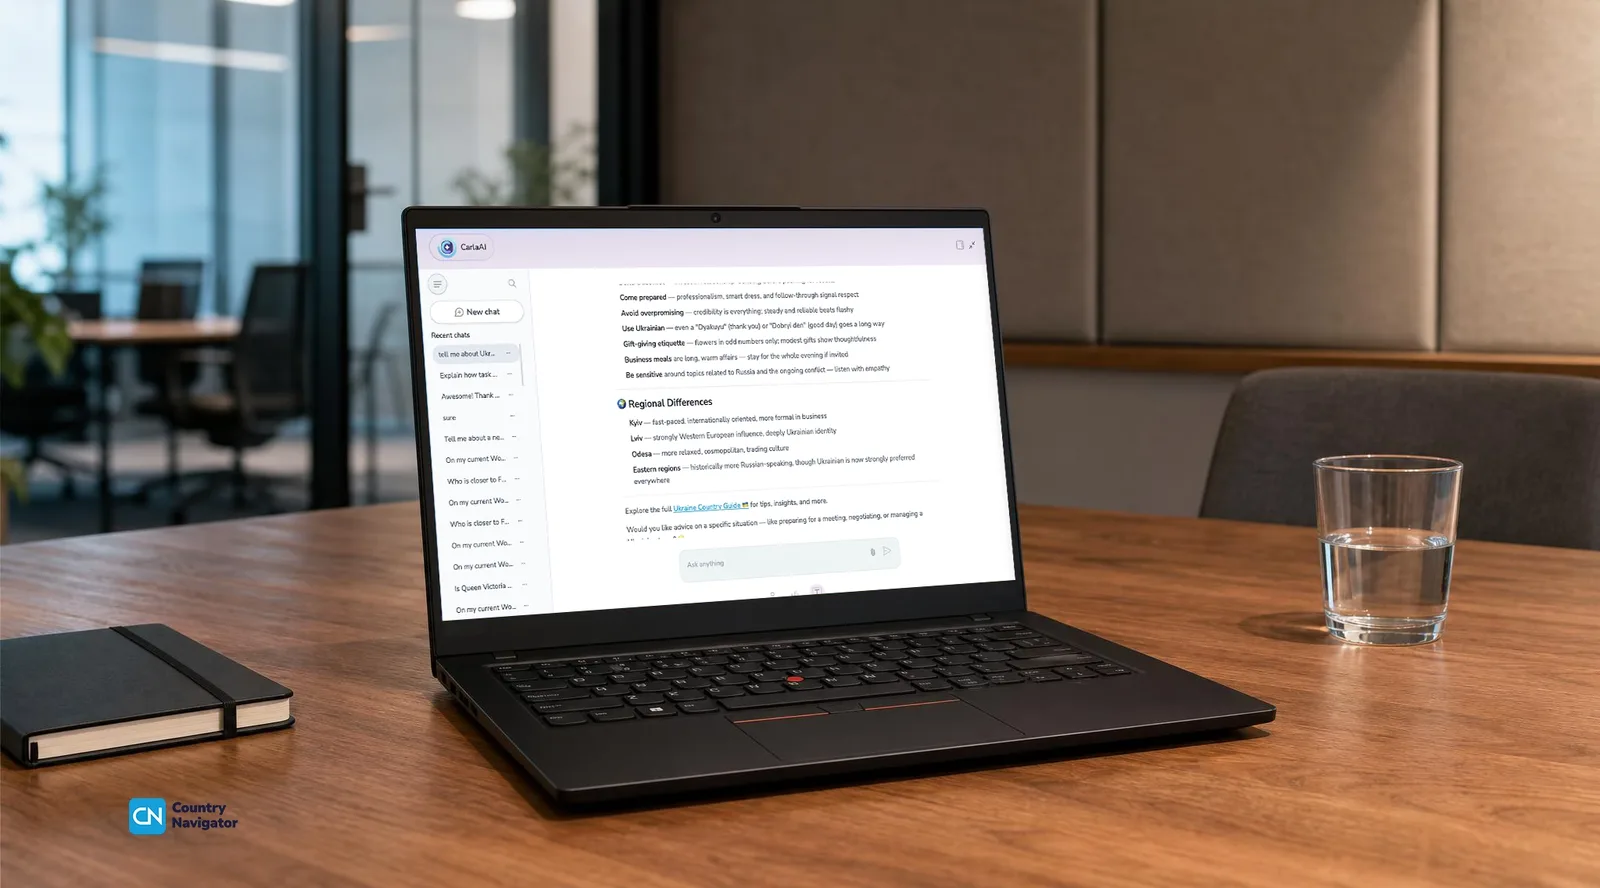
Country Navigator
A decade-old monolith serving enterprise customers, rebuilt into services and given a production AI assistant, with the user base migrated without downtime.
- 0Downtime moving a decade-old platform
- 1 configReplaces the SSO setup only one person knew
- 10 yearsOf monolith rebuilt into services
What You Get From the Security Assessment
An attack surface map, a threat model naming the actors that matter, findings from the code and the cloud configuration traced to what they expose, a remediation plan ordered by reach and effort, and the evidence a customer questionnaire asks for. Security consulting services delivered as documents your team owns.
What Security Consulting Services Cover
Chosen against your platform, your compliance boundary, and what your own team will run afterwards, from the cloud account down to a security architecture consulting question about a single trust boundary.
Where accounts, roles, and keys are defined, and where most breaches start. The review covers who can reach what, how credentials rotate, and whether a compromised role stays contained.
 AWS
 Microsoft Azure
 Google Cloud
 Okta
 Keycloak
 HashiCorp Vault
Frequently Asked Questions
What technical leads ask about security audit services before booking one.
 What is security consulting?
What does a security consultant do?
What do security consultants do?
What is a cybersecurity consultant?
How do cybersecurity advisory services help a small business?
What does security consulting cover?
How is this different from a penetration test?
What do we get at the end?
Can you review a system already in production?
Do you help with SOC 2 or HIPAA?
How long does it take?
What does it cost?
What does a cyber security consulting company do?
From a Questionnaire You Cannot Answer to a Plan You Can Work
Tell us what the system exposes and what triggered the question, whether that is a customer, an auditor, or a device in the field. You get an assessment scope, a timeline, and an exact price, the way every security consulting services project at Hygge starts.
Tell Us What Keeps You Up About Security
Share the systems, the data you hold, and the questionnaire or audit you are preparing for.
Get a First Consultation
We review your cloud, application, and pipeline exposure for anything that would change scope, cost, or timeline.
Receive a Detailed Proposal
A scoped plan with the approach, timeline, and cost, built around your actual risk surface.